Security architecture
Platform architecture
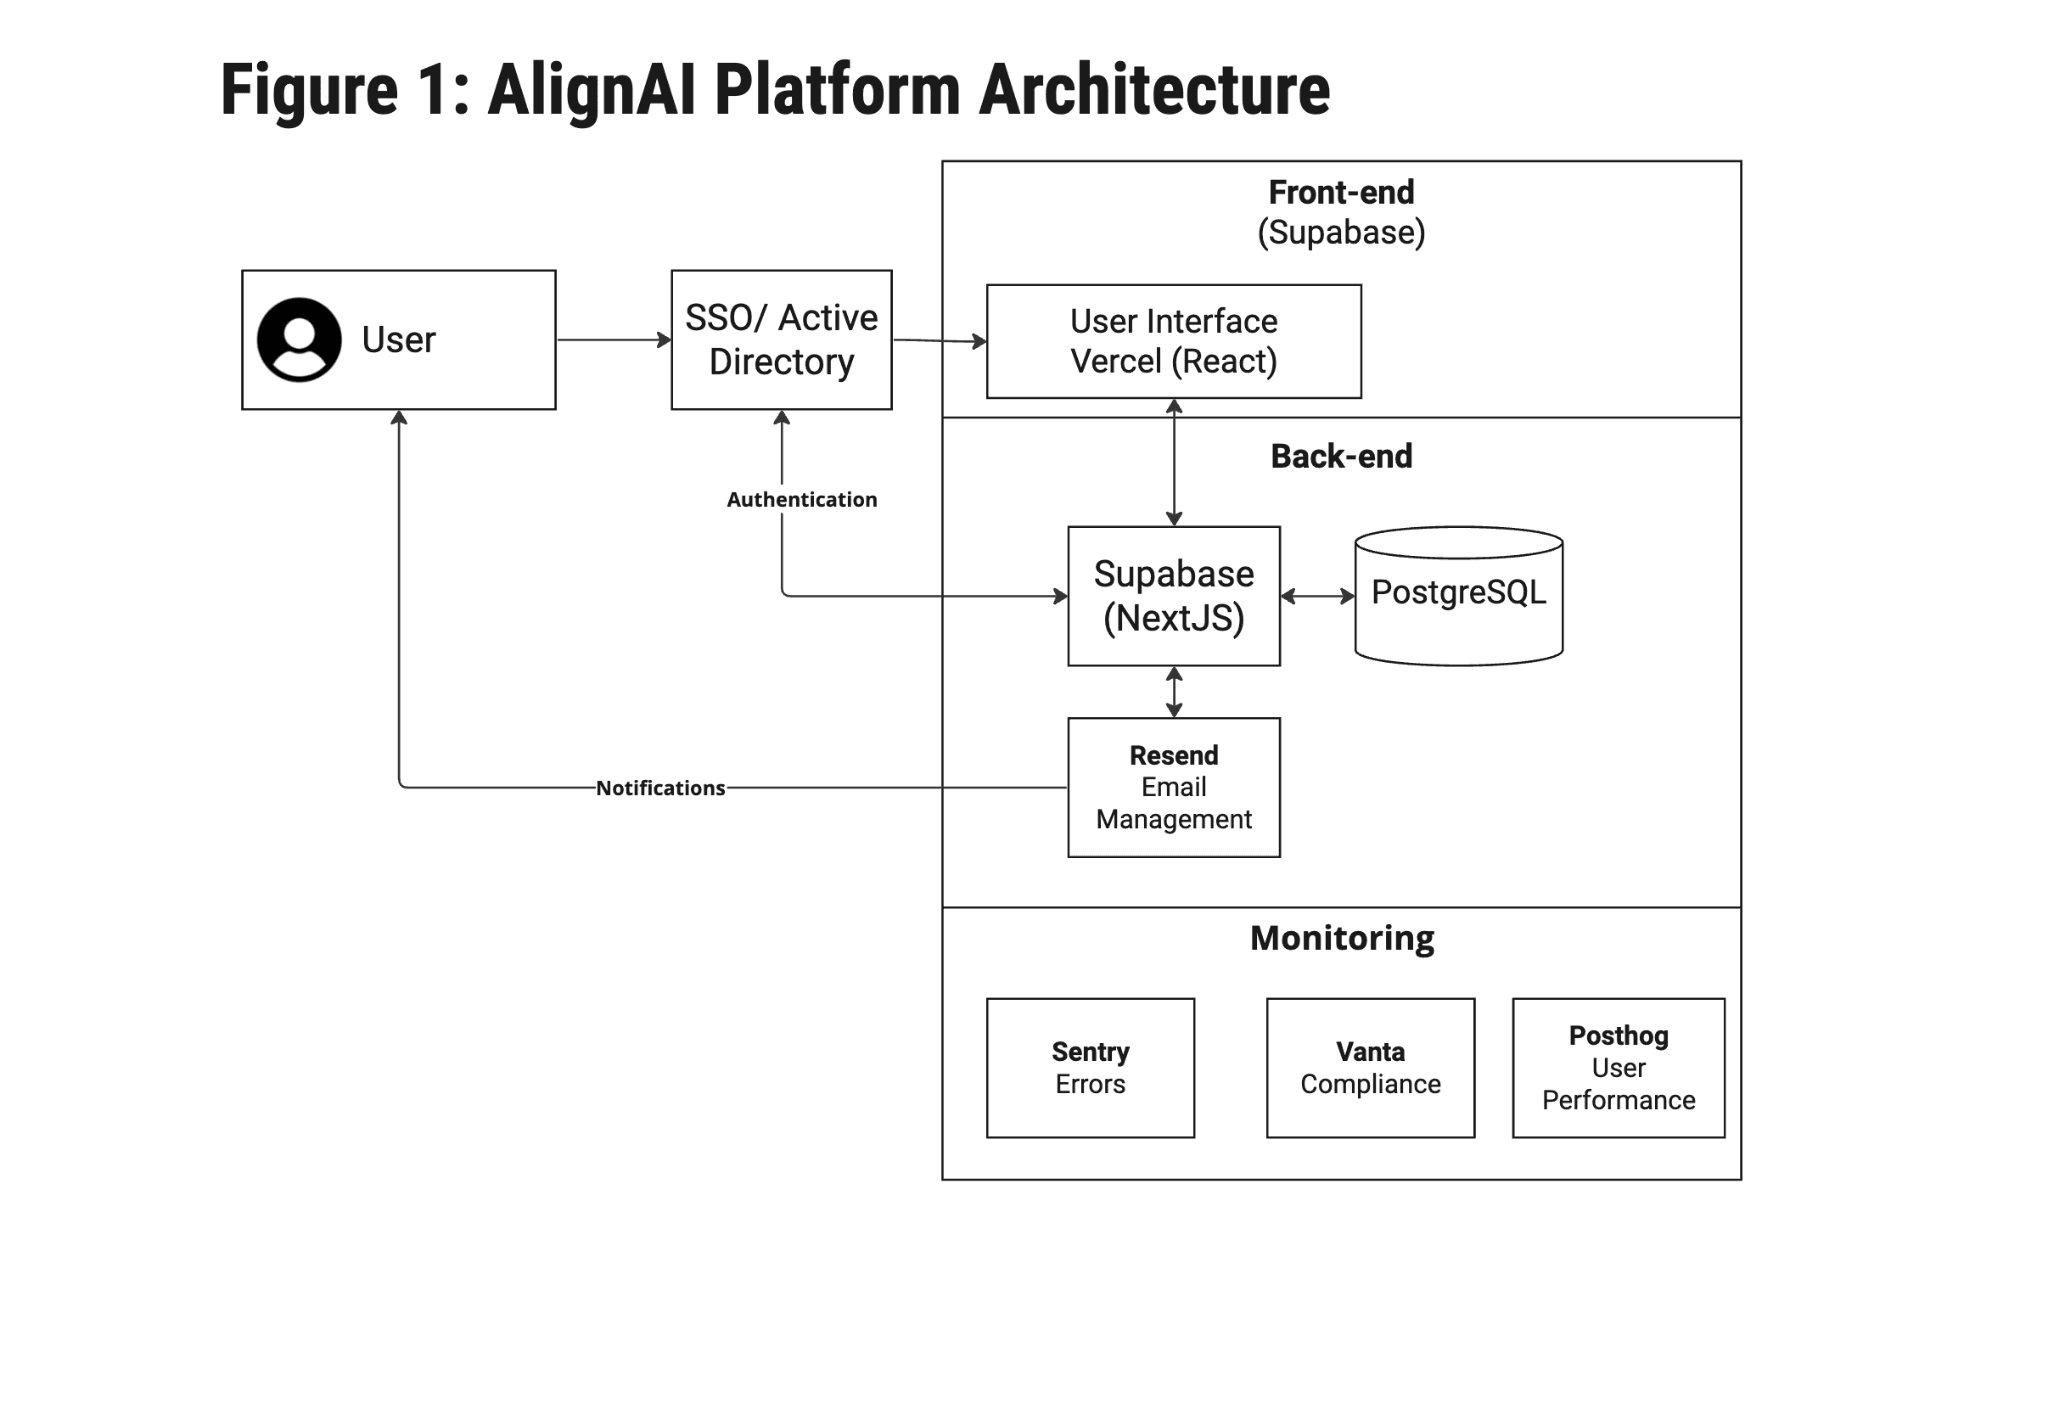
| Layer | Component | Role |
|---|---|---|
| Identity | SSO / Active Directory | Every user authenticates against your identity provider before reaching the application — see Single sign-on. |
| Front end | Vercel (React/Next.js) | Static and serverless UI hosting, global distribution, edge caching. |
| Back end | Supabase (Next.js API layer) | Application server, real-time layer, authentication, storage, and instant API. |
| Database | PostgreSQL (via Supabase) | Primary data store for use cases, solutions, and platform data. |
| Notifications | Resend | Outbound transactional/notification email. |
| Error monitoring | Sentry | Application error and exception tracking. |
| Compliance monitoring | Vanta | Automated security-control monitoring and SOC 2 evidence collection. |
| Product analytics | PostHog | User behavior and performance analytics. |
| AI / LLM | Azure OpenAI | Hosts the primary LLM used by the platform today. |
| AI / LLM (evaluation) | Anthropic Claude | Being evaluated for additional use cases; not yet a primary processing path. |
Where data actually goes
- Application data (use cases, solutions, custom fields, comments, audit history) is stored in PostgreSQL, managed by Supabase. Supabase also handles authentication and storage for the platform.
- AI-generated content (summaries, risk scoring, MCP tool responses) is processed through Azure OpenAI.
- Notification content (email bodies, which may reference use case names or statuses) passes through Resend.
- Error monitoring (Sentry) and product analytics (PostHog) capture application telemetry (stack traces, usage events) as part of normal operation.
- Employee/HR data, where used at all, is limited to what’s needed for reporting roll-ups (e.g., a submitter’s manager for portfolio reporting) — sourced from your identity provider’s directory attributes at SSO time, or in some customer configurations from a scheduled Workday file import. AlignAI does not extract employee identity data from unrelated systems.
Encryption
AlignAI’s Cryptography Policy requires that cryptographic risk be formally assessed for data in processing and at rest, and that strong cryptography — implemented in line with industry standards including NIST SP 800-57 — be applied wherever encryption is used, with documented key-management procedures. Customer and confidential data in storage or transit over a public network must use current, vendor-recommended cipher configurations.
Encryption at rest for AlignAI’s Supabase-hosted data stores has been independently verified as part of AlignAI’s SOC 2 Type II examination, alongside TLS in transit.
Hosting and tenancy
AlignAI runs on AWS, hosted in the US East region. This is the underlying cloud infrastructure beneath the Supabase (backend/database) and Vercel (frontend) platforms shown in the architecture diagram above — both of those managed platforms run on AWS themselves.