Single sign-on
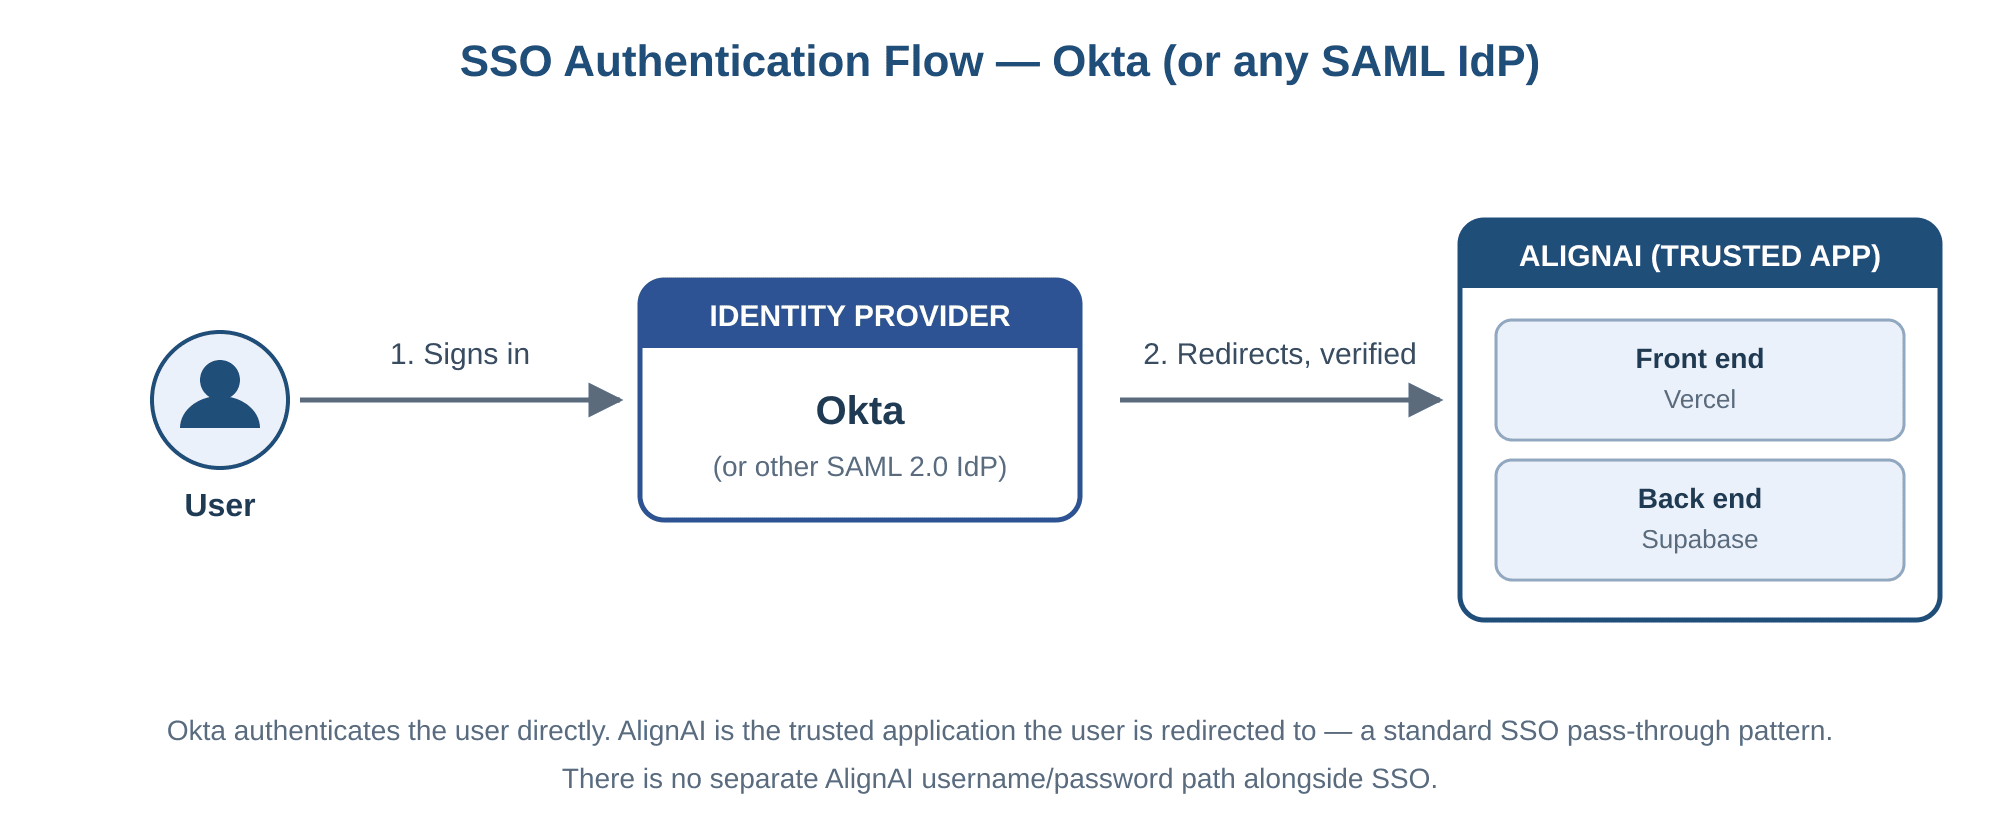
Every UI sign-in is routed through SSO before it reaches the application — a user authenticates against your identity provider first, and only then reaches the AlignAI front end (Vercel) and back end (Supabase). There is no separate AlignAI username/password path for UI login sitting alongside SSO.
AlignAI works with Okta and other SAML-based identity providers as a standard trusted-app integration. Your identity provider is the authentication gateway: it verifies the user, and AlignAI is the trusted application they’re redirected to once that verification is complete. This is a pass-through pattern — AlignAI doesn’t build custom integration work per identity provider.
Last updated on